Binance's $6.3B theft: what its own report says happened
Binance's own report: about $6.34B left its hot wallets on 29 Oct 2026. How the attackers got in, what is still open, and what to do.
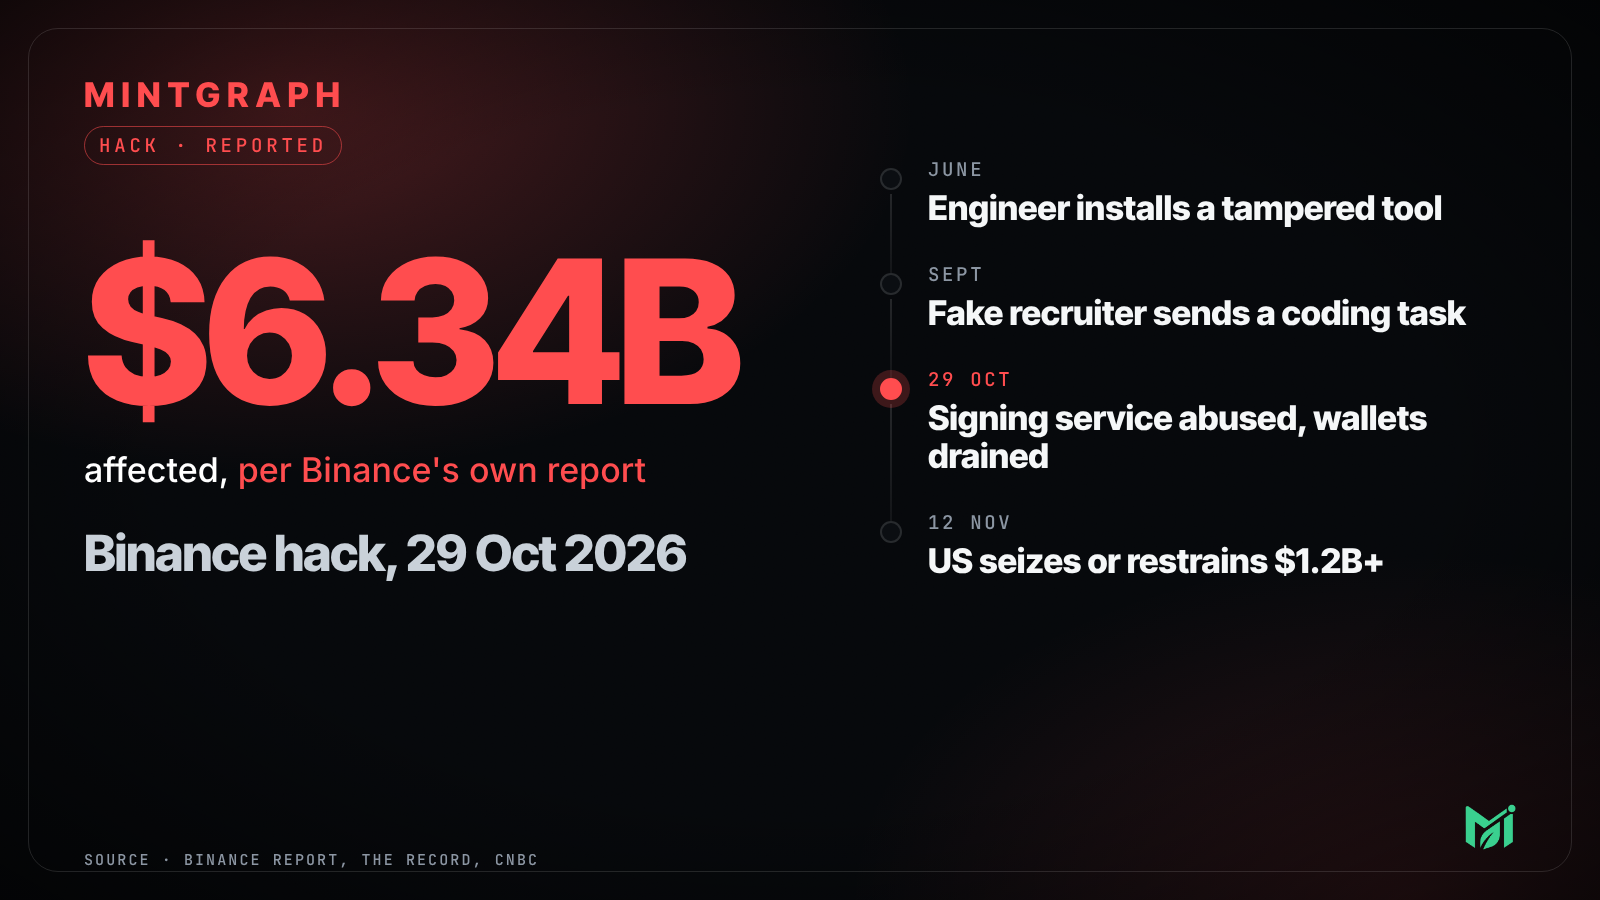
What Binance says happened
- 29 Oct, 20:05 to 20:09 UTC: five hot wallets sent 233.46 million XRP to an attacker address. Later transfers took about 970,500 SOL, 44.2 million OP, 18,270 BTC and, last, 2,961.9 ETH (final one confirmed at 23:56 UTC). (REPORTED, Binance report, 3 Nov)
- How the money moved: the attacker got into an internal wallet signing service and sent transactions outside the normal withdrawal process. It then used an Ethereum feature called EIP-7702 to give a contract of its own partial control over a hot wallet. (REPORTED, same report)
- Why it took hours to stop: pausing withdrawals did not cancel those on-chain permissions, and the hot wallet used a shared-key setup with no single key to revoke them. Binance wrote a special procedure and cleared the delegation at 00:10 UTC on 30 Oct. (REPORTED, same report)
- Size: about $6.34B affected, about $2.85B frozen or intercepted, per Binance. The US Justice Department says it got court approval to seize or restrain more than $1.2B of the stolen funds. (REPORTED, Binance; The Record, 12 Nov)
How the attackers got in, per Binance
Binance calls it a multi-stage campaign, not a single phishing click.
- June: an engineer searched for a popular AI coding tool and installed a tampered copy through Homebrew. Binance replaced the device, but the person's role and team were now known to the attacker.
- September: another engineer was approached through a real job site by a fake "project director", then interviewed twice, and told to download a coding "assignment". It ran malware that security tools did not catch at the time.
- 20 Oct: the attacker used an internal AI tool on that computer to reach a wallet DevOps engineer and found a deployment token.
- 29 Oct: between 17:15 and 19:56 UTC the attacker used those credentials to deploy a container and launch the theft.
Binance says its team stopped 57 suspected North Korea-linked attempts in 2026 before this one. (REPORTED, Binance report)
- Tampered toolJune, one laptop
- Fake recruiterSept, job site
- Malware taskcoding assignment
- AI tool pivot20 Oct
- Signing service29 Oct, credentials reused
- Funds outhot wallets
Binance says it was a chain of small steps by people, not one smart-contract bug.
Source · Binance report, 3 Nov 2026
Who is blamed
Binance cites an FBI alert saying North Korea is responsible. The Record reports that Binance and the FBI both name the group TraderTraitor. No court has ruled on it. (REPORTED)
What it means for you
- Exchange coins are the exchange's keys. This was theft from the company's wallets, not from user wallets. Binance says it has replenished 98% of the affected assets as of 31 Oct, checkable on its Proof of Reserves page. (REPORTED)
- Scams follow headlines. Binance told users not to trust unofficial links, messages or requests for account information. Any "refund", "compensation" or "verify your account" message after this event is a scam until you type the exchange's address yourself and check there. (MintGraph guidance)
- The first step was a person, not code. Fake recruiters and "just run this repo" tasks are how it started. If you work with wallets, never run a stranger's assignment on the same computer.
More: Where stolen crypto goes (Bitget case) and How to check if a crypto airdrop is legit.
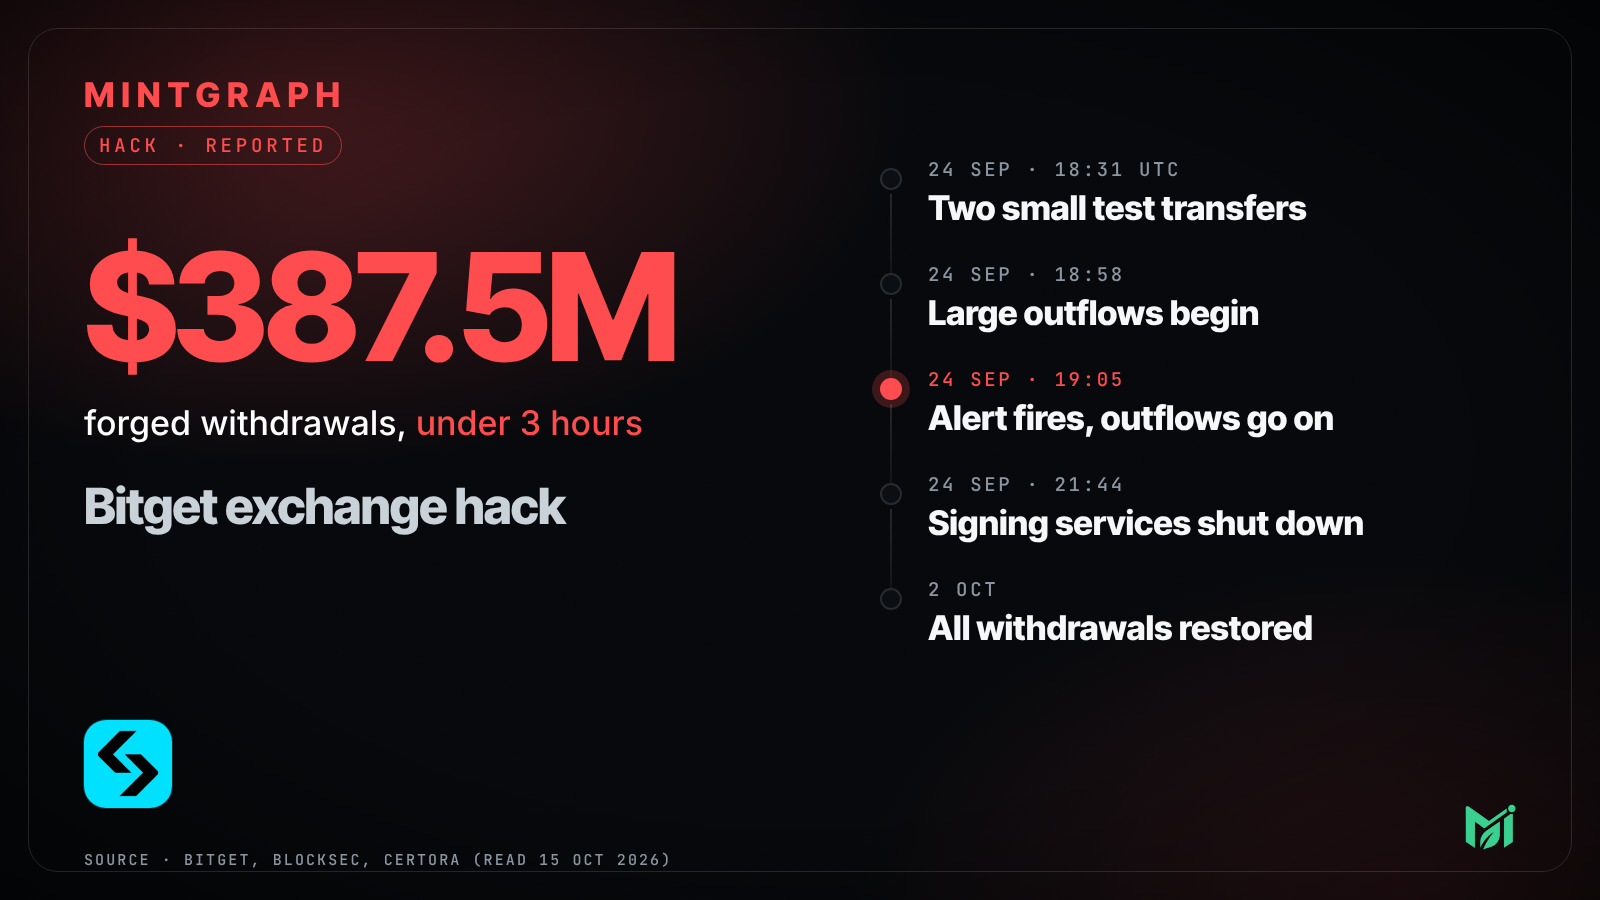 Research noteWhere stolen crypto goes: the $388M Bitget hack, step by step
 GuideHow to check if a crypto airdrop is legit
Questions
Did users lose money?
Binance says it will cover all losses from its own funds and the SAFU fund. Withdrawals were paused, then reopened in stages. We have no independent audit of that claim yet.
Was it a bug in a smart contract?
Not according to Binance. It says an internal signing service was abused, and an Ethereum permission feature was used to keep control after withdrawals stopped.
Is North Korea confirmed?
Binance and the FBI say so, and blockchain firms agree. A court has not tested it.
What should I do now?
Use only official channels, ignore refund offers, turn on app-based or hardware two-factor, and keep only what you trade on an exchange.
This is research and safety guidance, not financial advice. Facts checked 13 November 2026.
One next step
Read Binance's own reportx.com
Sources
- Binance: 29 October Security Incident, Initial Findings and Response Update
- The Record: Feds announce seizure of $1.2 billion from Binance theft (12 Nov 2026)
- CNBC: Binance says 90% of hack losses are covered (31 Oct 2026)
- TechCrunch: Binance pauses withdrawals (29 Oct 2026)
- Elliptic: North Korea is minting meme coins to launder the Binance hack (10 Nov 2026)
Sources
- Binance: 29 October Security Incident, Initial Findings and Response Update x.com
- The Record: Feds announce seizure of $1.2 billion from Binance theft (12 Nov 2026) therecord.media
- CNBC: Binance says 90% of hack losses are covered (31 Oct 2026) www.cnbc.com
- TechCrunch: Binance pauses withdrawals (29 Oct 2026) techcrunch.com
- Elliptic: North Korea is minting meme coins to launder the Binance hack (10 Nov 2026) www.elliptic.co
Comments
Sign in with Telegram through Ari to comment, reply and react. Use the plain page
Comments go live at once and are checked automatically. Links are shown as text. Never post a seed phrase or private key. Ari is MintGraph’s assistant. Her replies here are written or checked by the MintGraph team.
No comments yet. Be the first.