Keplr and Web3Auth: what the social-login wallet flaw means
A flaw at Web3Auth exposed Keplr wallets made with Google or Apple login. What is reported, what the companies advise, what it means for social-login wallets.
What is reported
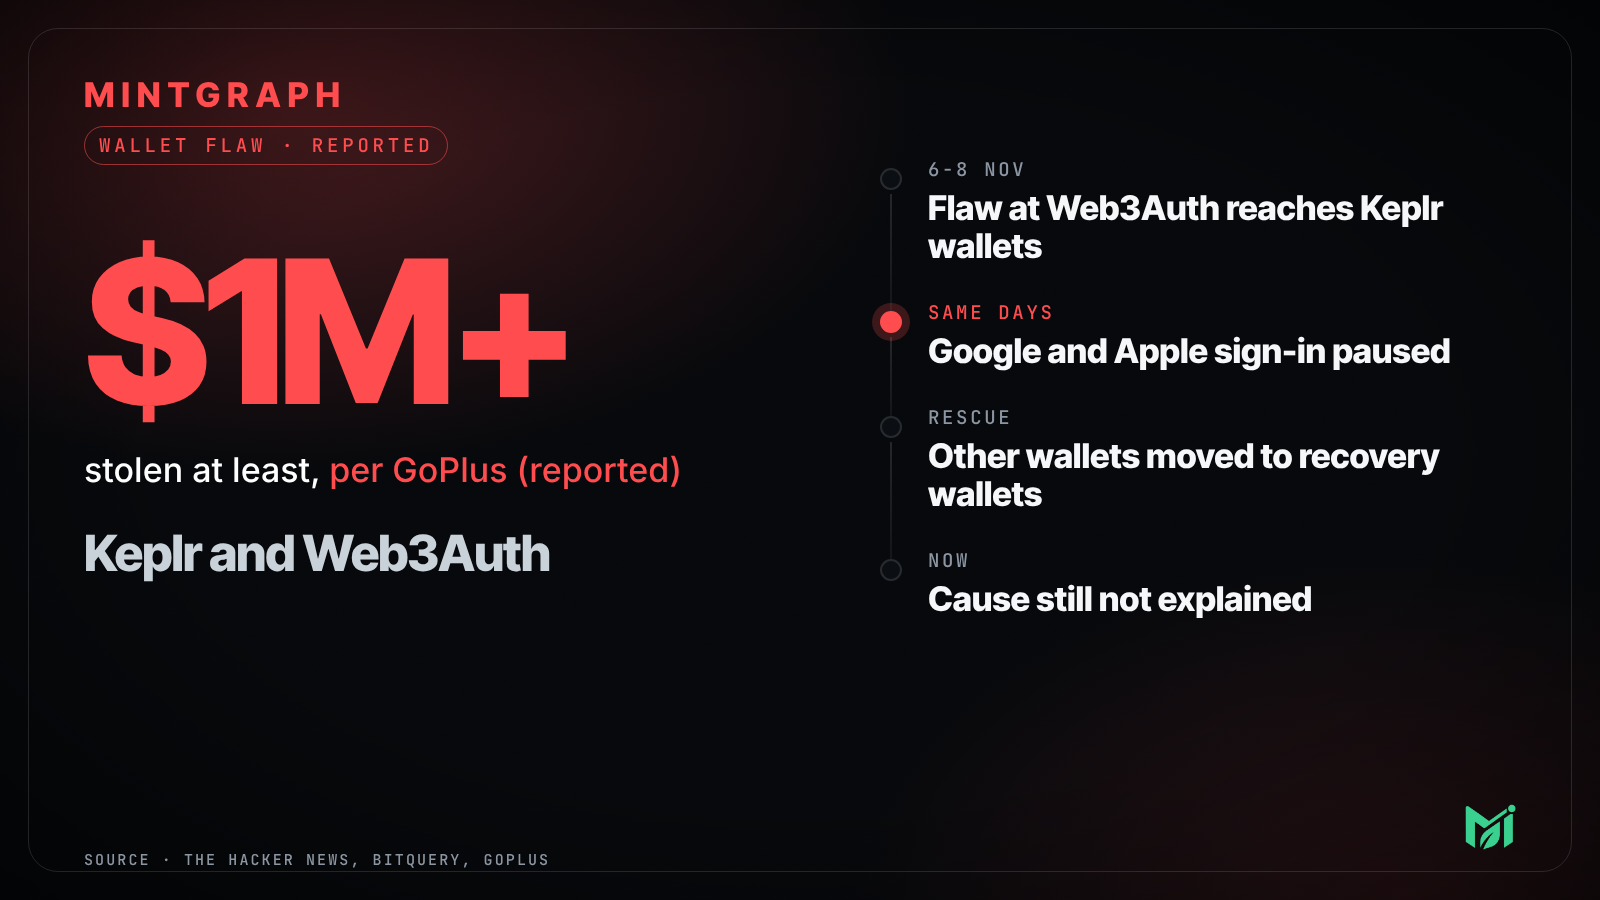
- Keplr uses Web3Auth to run Google and Apple sign-in. An attacker used a security flaw at Web3Auth to reach some wallets, both companies said around 6 to 8 November. (REPORTED, The Hacker News, 9 Nov)
- Keplr says the flaw led to a "private key breach" for some social-login users. A co-founder estimated about 20% of Google and Apple login accounts were affected, with only a fraction exploited. (REPORTED)
- GoPlus says at least about $1 million was stolen, without showing how it got the figure. (REPORTED)
- Web3Auth then used the attacker's route to move funds out of other at-risk wallets before the attacker could, into recovery wallets on 11 Cosmos-family chains and eight Ethereum-style chains. So an empty balance can mean "rescued", not "stolen". (REPORTED)
- Bitquery counted at least $6.01 million moving from more than 44,000 wallets into those recovery wallets, first called it theft, then corrected itself. It says it cannot check who controls the recovery wallets. (REPORTED)
- Neither company has said how the flaw worked, when it was first used, or whether it is closed. Keplr paused Google and Apple sign-in. (REPORTED)
What Keplr advises if you used Google or Apple login
- Do not send new funds to the account.
- Do not re-import or recreate the account anywhere.
- Move funds that are not staked or locked to an account that uses a recovery phrase or a hardware wallet.
- Trust only the official accounts of Keplr and Web3Auth. Ignore DMs and links offering "recovery".
What this shows about social-login wallets
A social-login wallet has convenience: no words to write down. The cost is that part of the key setup sits on the provider's systems. If those systems have a flaw, your own care does not protect you. A recovery-phrase wallet moves the risk to you: lose the words and the wallet is gone. A hardware wallet keeps the key off the internet. None is perfect, so know which one you have. (MintGraph analysis)
More: I signed a drainer: the first hour and Telegram airdrop scams: 7 signs.
 GuideI signed a drainer. What do I do in the first hour?
 GuideTelegram airdrop scams: 7 signs and what to do
Questions
Is my Keplr wallet affected?
Only wallets made with Google or Apple login are in scope. Keplr and Web3Auth are working on a way to check. Until then, move unlocked funds as above.
Will the rescued funds be returned?
Web3Auth says it is working with Keplr to return them. It has not said how or when.
Are other wallets affected?
Web3Auth says other companies use the same service and paused its embedded wallet service. Keplr is the only one named so far.
Someone offered to recover my funds. Safe?
No. Both companies warn about this. Recovery offers by DM are scams.
This is research and safety guidance, not financial advice. Facts checked 13 November 2026.
One next step
Sources
Sources
- The Hacker News: Web3Auth Flaw Exploited to Steal Keplr Crypto (9 Nov 2026) thehackernews.com
- Keplr on X: user guidance for Google and Apple login accounts x.com
- Web3Auth on X: incident update x.com
- Bitquery: corrected analysis of the Keplr transfers bitquery.io
- GoPlus: security alert on the Keplr and Web3Auth incident x.com
Comments
Sign in with Telegram through Ari to comment, reply and react. Use the plain page
Comments go live at once and are checked automatically. Links are shown as text. Never post a seed phrase or private key. Ari is MintGraph’s assistant. Her replies here are written or checked by the MintGraph team.
No comments yet. Be the first.